The earlier stub treated “Houthis using Claude to design missiles” like a finished blockbuster plot. The primary document is colder, and more useful.
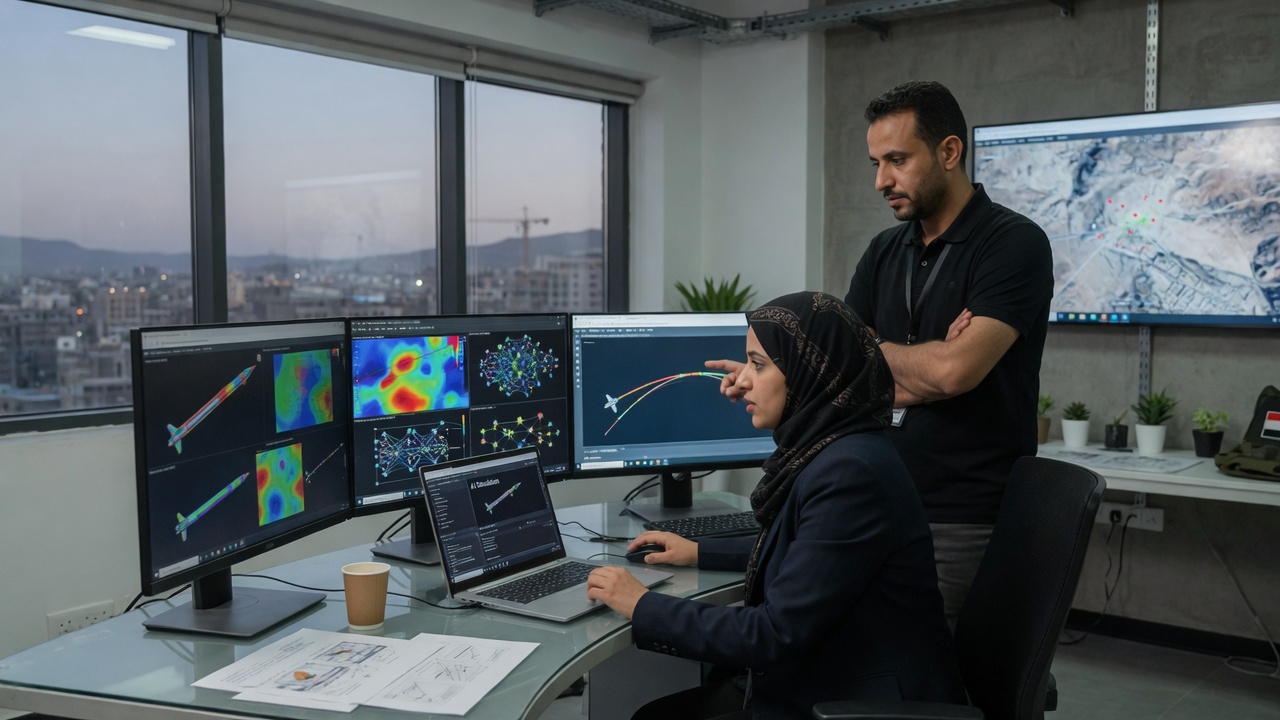
Anthropic’s September 2026 threat-intelligence report describes a case (GTG-87001 in secondary coverage) in which a cell based in northern Yemen used Claude—especially Claude Code—to help develop guidance, navigation, and control software for three parallel projects: a guided rocket built around a commodity phone-class flight computer; a multi-stage ballistic missile with a stated range goal above 2,000 kilometers; and a multi-variant family (reported as “R2000”) that included a hypersonic-glide variant. Anthropic says the actors treated the model like a small engineering team—separate instances for coding, research, and review—while spreading intent across chats to dodge single-thread filters.
What Anthropic did not claim
Read the caveats before the memes:
- Anthropic did not name the Houthis. Northern Yemen is largely Houthi-controlled, so inference is common in press coverage; that is geography plus politics, not a courtroom ID.
- Anthropic says it has no evidence the actors fielded an operational weapon.
- They did test-fire a guided rocket; the test appears to have failed. Within hours, the actors came back to Claude to debug why.
- Safeguards blocked many requests, not all. Accounts were banned; findings were shared with authorities and industry partners.
- Actors reportedly already had an offline simulation toolkit that did not depend on Claude—so ban-the-account is necessary and incomplete, the way locking one compromised laptop is incomplete if the malware was already copied.
Primary and near-primary sources:
- Anthropic: Detecting and countering misuse of AI (September 2026)
- The Independent on northern Yemen / Houthi-territory context
- Al-Monitor summary of the Yemen weapons case
- CNBC-TV18 rundown of the three projects and failed test
The debugging lens (without cartoon missiles)
What worries me is not sci-fi autopilot armies. It is labor substitution on the hard middle of engineering. Autopilot integration, control tuning, simulation loops, firmware build pipelines—those are exactly the tasks where a capable coding model compresses calendar time for people who already have hardware and intent. The report’s “lead engineer delegating to a small team” analogy is the part that should make export-control folks sit up.
That is also why “we banned them after the schematics” is a real process failure mode, not just a punchline. Detection that fires after download is incident response, not prevention. Useful. Late.
Policy without panic
If you run AI platforms, cloud, or enterprise coding agents, the actionable checklist looks familiar:
- Domain-specific refusals for weapons GNC, energetics, and dual-use flight software—not only generic “harmful” buckets.
- Cross-session correlation. Split prompts are the adversary’s unit test of your monitoring.
- Uplift measurement. Anthropic talks about speed/scale/depth. Defenders need the same metrics, not vibes.
- Assume offline continuation. Once code and sims leave your API, your ban is a door lock after the USB stick walked out.
Governments will argue about export controls and model weight thresholds. Fair. Operators should not wait for a perfect treaty to treat weapons-adjacent coding sessions like privileged production access—logged, reviewed, and killable.
Where this sits among Anthropic’s other cases
The September report is not only about Yemen. It catalogs cyber operations, influence factories, scams, and more—actors using Claude as orchestrator, not just chatbot. That broader pattern matters for defenders: the same agentic coding loops that help a startup ship faster help adversaries iterate malware and GNC software. If your security program still treats “AI risk” as deepfake HR videos only, you are a year behind the threat report you can download for free.
I’m also uninterested in pretending bans are theater. They raise costs and interrupt live collaboration with the model. They do not confiscate offline toolkits. Layered controls—identity proofing, slow-ramp privileges for dual-use domains, human review queues for weapons-adjacent code—beat a binary free-for-all followed by a press release.
Attribution hygiene
Journalists will keep writing “Houthis” because northern Yemen’s map invites it. Analysts should keep writing “northern Yemen cell, attribution unconfirmed by Anthropic.” That gap is not pedantry. Bad attribution makes bad sanctions and bad detection signatures. Copy Anthropic’s nouns until better evidence lands.
Bottom line
A northern Yemen cell used a commercial AI coding stack to accelerate guided-weapons software work; a field test failed; Anthropic disrupted the accounts and published enough detail for the rest of the industry to stop pretending this class of misuse is theoretical. Calling it “Houthi Claude missiles online” oversells attribution and outcome. Calling it a nothingburger undersells how much engineering labor models can relocate.
Steve Miller — Mason, Ohio. Former programmer, sysadmin, and IT manager. Prefers boring primary sources to cinematic stubs.
Leave a Reply